Securing Your WordPress Site: Preventing Plugin Vulnerabilities
Key Takeaways
- Plugins extend WordPress, but each one is a potential attack vector. The common threats are cross-site scripting, SQL injection, CSRF, remote code execution, and privilege escalation.
- Most breaches trace back to outdated or abandoned plugins. Update on a schedule and remove anything no longer maintained, since unpatched code is the easiest way in.
- Audit your plugin footprint. Running fewer, well-coded plugins reduces compatibility conflicts and shrinks the surface attackers can probe.
- Tighten user permissions. Give each account only the access it needs so a single compromised login cannot install plugins or escalate to admin.
- An exploited plugin can cost you data, revenue, and reputation. Proactive maintenance, input sanitization, and least-privilege access are far cheaper than recovery.
1. Introduction
WordPress plugins are essential for extending website functionality, but they can also introduce security risks if not properly managed. Unpatched vulnerabilities can lead to data breaches, malware infections, and compromised user experiences. At Brightter, we prioritize website security by implementing best practices to prevent plugin-related threats. This guide explores common plugin vulnerabilities, their technical implications, and the proactive steps to secure your WordPress site.
2. Understanding WordPress Plugin Vulnerabilities
Plugins enhance WordPress capabilities, but poor maintenance or outdated software can make them a gateway for cyber threats. The most common vulnerabilities include:
- Cross-Site Scripting (XSS): Attackers inject malicious scripts into web pages, stealing user data or defacing content. This occurs when input fields, forms, or URL parameters are not properly sanitized.
- SQL Injection (SQLi): Exploiting weak database queries to insert malicious SQL statements, which can grant unauthorized access to sensitive data, alter records, or even delete critical site information.
- Cross-Site Request Forgery (CSRF): Manipulating authenticated users into executing unintended actions, such as account modifications or unauthorized financial transactions.
- Remote Code Execution (RCE): Attackers exploit poorly coded plugins to execute arbitrary code, leading to full site takeover.
- Privilege Escalation: Exploiting vulnerabilities that allow unauthorized users to gain administrative access to a WordPress site.
Ignoring these vulnerabilities can lead to hacked websites, lost revenue, and damage to brand reputation.
3. What Causes Plugin Vulnerabilities?
Several factors increase security risks:
- Outdated Plugins: Security patches are frequently released, and failing to update plugins leaves sites vulnerable to exploits.
- Abandoned Plugins: Plugins without active development can no longer receive security updates, making them a liability.
- Poor Coding Practices: Plugins with unfiltered input fields, weak authentication protocols, and missing nonce verification are particularly prone to attacks.
- Excessive Plugin Use: Running too many plugins increases the risk of compatibility issues and security flaws, as each plugin represents a potential attack vector.
- Weak User Permissions: Assigning excessive privileges to users can allow unauthorized modifications or the installation of harmful plugins.
4. The Impact of Exploited Plugin Vulnerabilities
If vulnerabilities are not addressed, websites can suffer from:
- Data Breaches: Exposure of customer data, including personally identifiable information (PII) and payment details, leading to legal and financial repercussions.
- Malware Infections: Hackers inject malicious scripts or backdoors, infecting visitors' devices and spreading malware.
- Website Defacement: Unauthorized modifications to content or site layout, damaging brand credibility and user trust.
- SEO Penalties: Search engines may blacklist infected websites, drastically reducing organic traffic and affecting rankings.
- Resource Hijacking: Attackers may use compromised plugins to run cryptojacking scripts, consuming server resources for mining cryptocurrencies.
5. How to Secure Your WordPress Plugins
a. Use a Secure Hosting Environment
A robust hosting provider with built-in security measures, firewalls, malware scanning, and DDoS protection helps safeguard your site. Managed WordPress hosting solutions offer proactive security monitoring, automatic backups, and server-level caching.
b. Keep Plugins Updated
Regularly updating plugins ensures that security patches are applied. Enable automatic updates where possible and manually verify major updates to avoid compatibility issues.
c. Remove Unused and Abandoned Plugins
Periodically audit installed plugins and remove those that are outdated or no longer maintained. Conduct code reviews or use third-party vulnerability databases to assess risks.
d. Choose Trusted Plugins
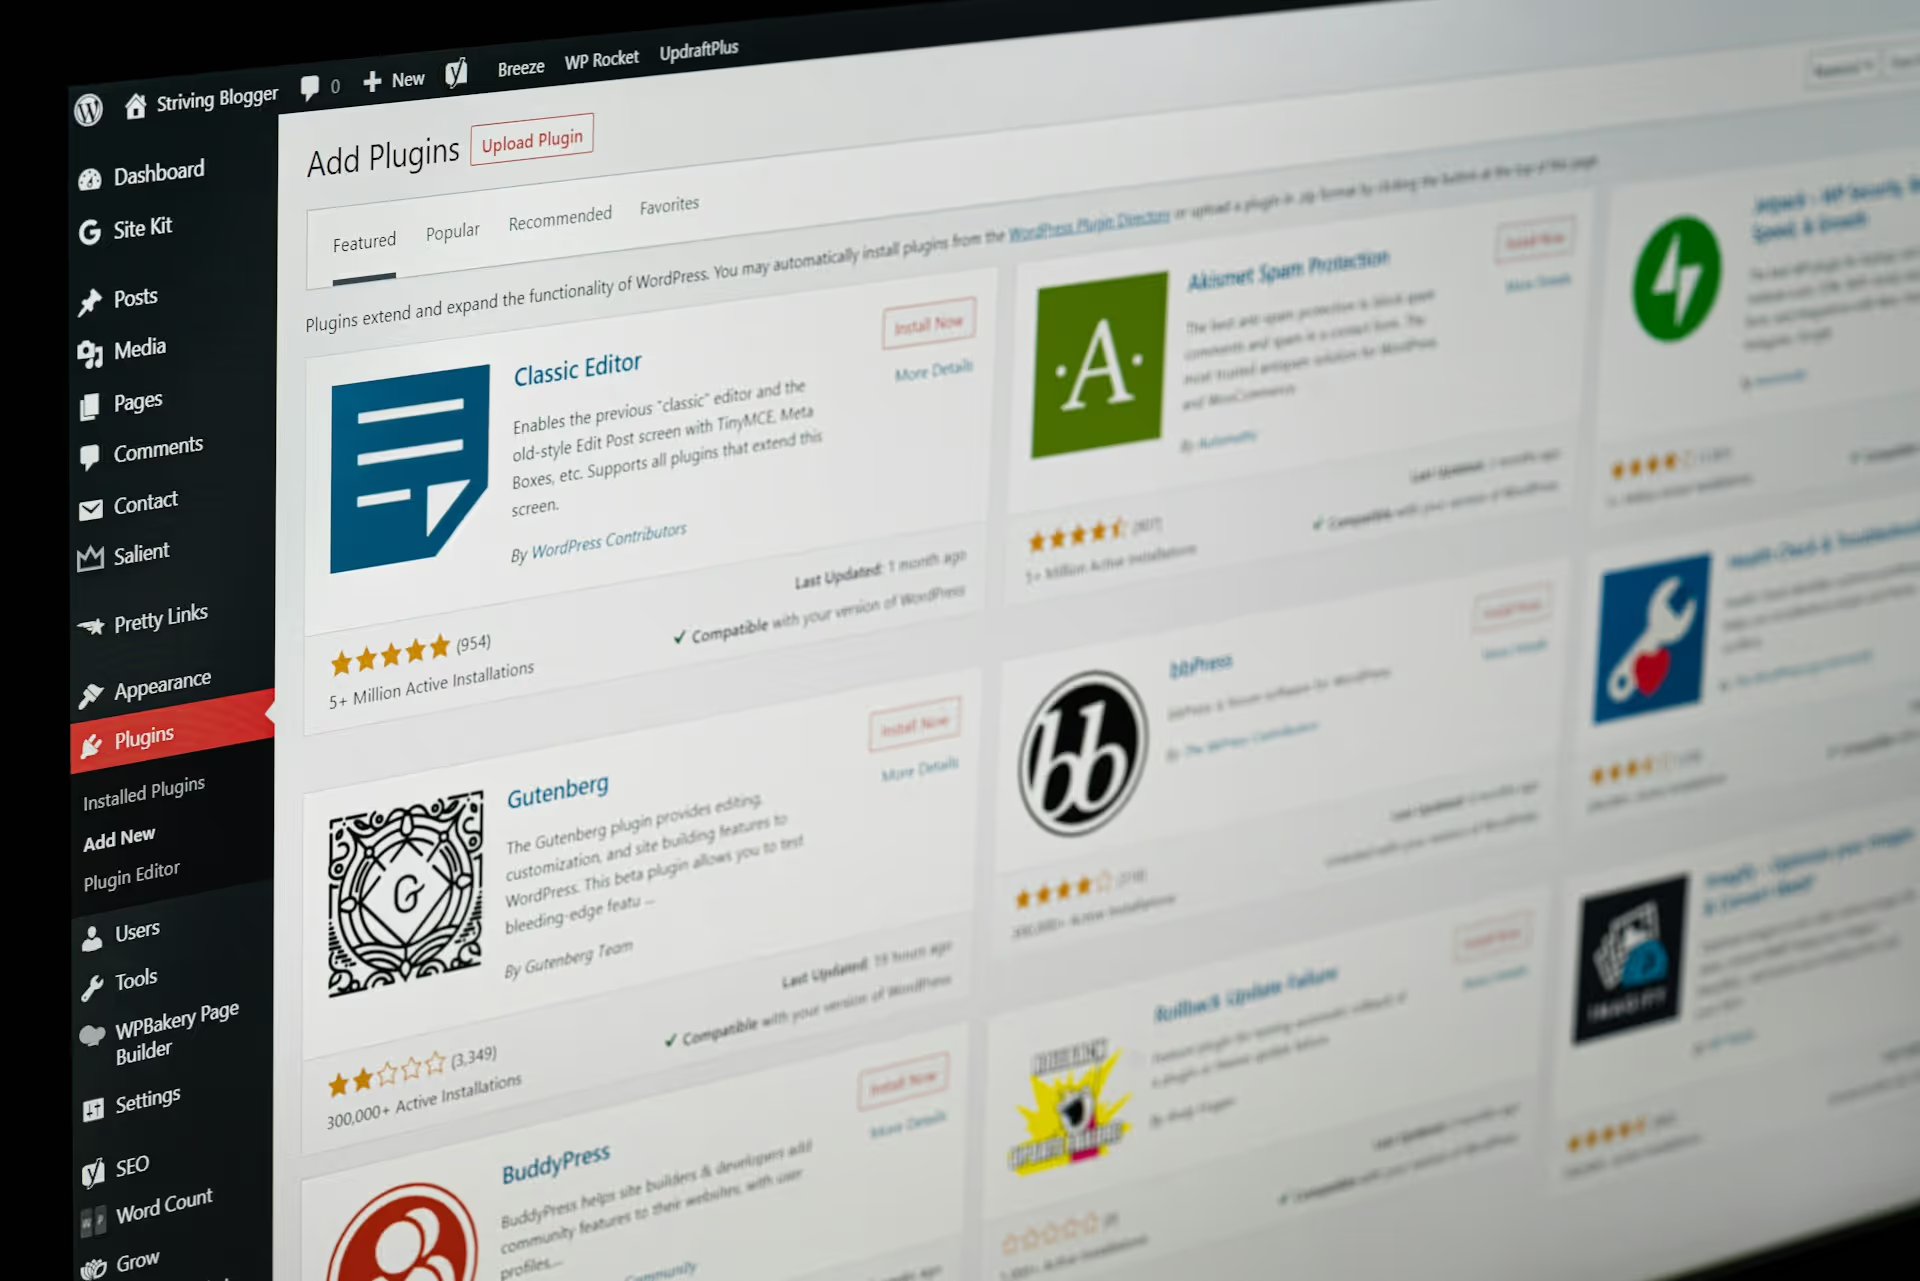
Only install plugins from reputable sources such as the WordPress Plugin Repository or verified developers. Check update frequency, active installations, and community feedback before installation.
e. Limit Plugin Usage
Use only the plugins necessary for your site’s functionality. Reducing the number of active plugins minimizes security risks, decreases attack vectors, and improves website performance.
f. Install Security Plugins
Security plugins like Wordfence, Sucuri, and MalCare scan for vulnerabilities, detect malicious code, and block suspicious activity. Implement security firewalls to prevent brute-force attacks and unauthorized API access.
g. Monitor Site Activity
Tracking login attempts, file changes, and plugin modifications can help detect suspicious behavior early. Use activity log plugins to maintain visibility over security events and set up real-time alerts.
h. Enforce Strong Authentication
Require strong passwords and implement two-factor authentication (2FA) for admin accounts to prevent unauthorized access. Restrict login attempts and use CAPTCHA to deter automated bots.
i. Regularly Scan for Malware
Perform periodic security scans to identify vulnerabilities before attackers exploit them. Automated scanning tools can help detect and remove potential threats, ensuring site integrity.
j. Backup Your Website Frequently
Regular backups ensure that if an attack occurs, your site can be restored quickly. Store backups in secure, off-site locations and use incremental backup solutions to minimize downtime.
k. Implement Proper User Role Management
Restrict administrative privileges and assign the least required permissions to each user. Ensure that only verified administrators can install or modify plugins.
l. Utilize Web Application Firewalls (WAFs)
Deploying WAFs adds an additional layer of security by filtering out malicious traffic before it reaches your website. Services like Cloudflare and Sucuri protect against SQL injections, XSS, and DDoS attacks
6. Final Thoughts
WordPress plugins play a crucial role in website functionality, but they also introduce security risks if not properly managed. By following best practices (such as keeping plugins updated, choosing secure hosting, enforcing authentication measures, and implementing proactive security solutions), you can protect your website from potential threats.
At Brightter, we specialize in WordPress security and optimization. If you're looking to fortify your site against plugin vulnerabilities, our team is here to help. Contact us today to enhance your WordPress security and ensure a safer, more resilient online presence.
Frequently Asked Questions
What are the most common WordPress plugin vulnerabilities?
The most common WordPress plugin vulnerabilities are Cross-Site Scripting (XSS), SQL Injection (SQLi), Cross-Site Request Forgery (CSRF), Remote Code Execution (RCE), and Privilege Escalation. Each exploits weak coding practices or unsanitized inputs to gain unauthorized access or compromise the site.
What causes WordPress plugin vulnerabilities?
Plugin vulnerabilities typically come from outdated plugins missing security patches, abandoned plugins no longer receiving updates, poor coding practices like unfiltered input fields or missing nonce verification, running too many plugins (each adds an attack vector), and weak user role permissions allowing unauthorized installations.
What happens if WordPress plugin vulnerabilities are exploited?
Exploited vulnerabilities can lead to data breaches exposing customer PII and payment data, malware infections that spread to visitors, website defacement damaging brand credibility, SEO penalties from search engine blacklisting, and resource hijacking where attackers use your servers for cryptojacking.
How can I secure WordPress plugins on my site?
Use a secure managed WordPress host with built-in firewalls and malware scanning, keep all plugins updated automatically, remove unused and abandoned plugins, install only trusted plugins from verified developers, deploy security plugins like Wordfence or Sucuri, enforce two-factor authentication, and use a Web Application Firewall (WAF).
Does Brightter help secure WordPress sites against plugin vulnerabilities?
Yes. Brightter provides WordPress security hardening covering plugin audits, vulnerability scanning, malware monitoring, WAF deployment, secure hosting setup, user role management, and backup strategies. We help businesses protect their WordPress sites against the full range of plugin-related threats.